The world of technology moves quickly, and 2026 has been no different. Staying on top of all the new changes can feel like a big challenge. This is especially true for busy leaders, smart investors, and the teams who make sure companies follow the rules. That’s why events like the recent Texas technology conference are so important. They bring everyone together to talk about the biggest topics.
This year’s Texas technology conference focused on many key areas. Think about how important new ideas in things like AI, cybersecurity, and even topics like quantum computing news today are. The conference also dove deep into how these new technologies affect business rules and laws. For example, discussions at events like the 2026 Texas Technology Summit covered how AI, systems, and culture all work together for the future of tech [1]. Other meetings, like the Dallas Technology Summit 2026, looked at managing AI-ready systems for demanding setups [2].
It’s clear that the Texas technology conference was a place for understanding important shifts. Leaders learned how to use new tech, investors saw where the market is headed, and compliance teams got updates on tricky areas like classified technologies in 2026. These discussions are key for staying ahead in a world where new rules for things like AI are always popping up. For instance, knowing how to handle AI and data for good is a big deal, as seen at the Texas Digital Government Summit 2026 [3].
With so much happening, it’s easy to feel lost in all the information. Our goal with this article is to give you clear, useful takeaways from the Texas technology conference. We want to connect the new rules and changes directly to how they affect your business. We aim to help you understand not just what happened, but what it means for you and your team right now.
Get clear daily AI updates from The AI Newsletter Worth Reading.
Top conference takeaways for tech leaders
The recent Texas technology conference shared many important lessons for leaders like you. These lessons touch on how to plan your business, what products to make, and how to follow new rules. Here are the main things you should know:
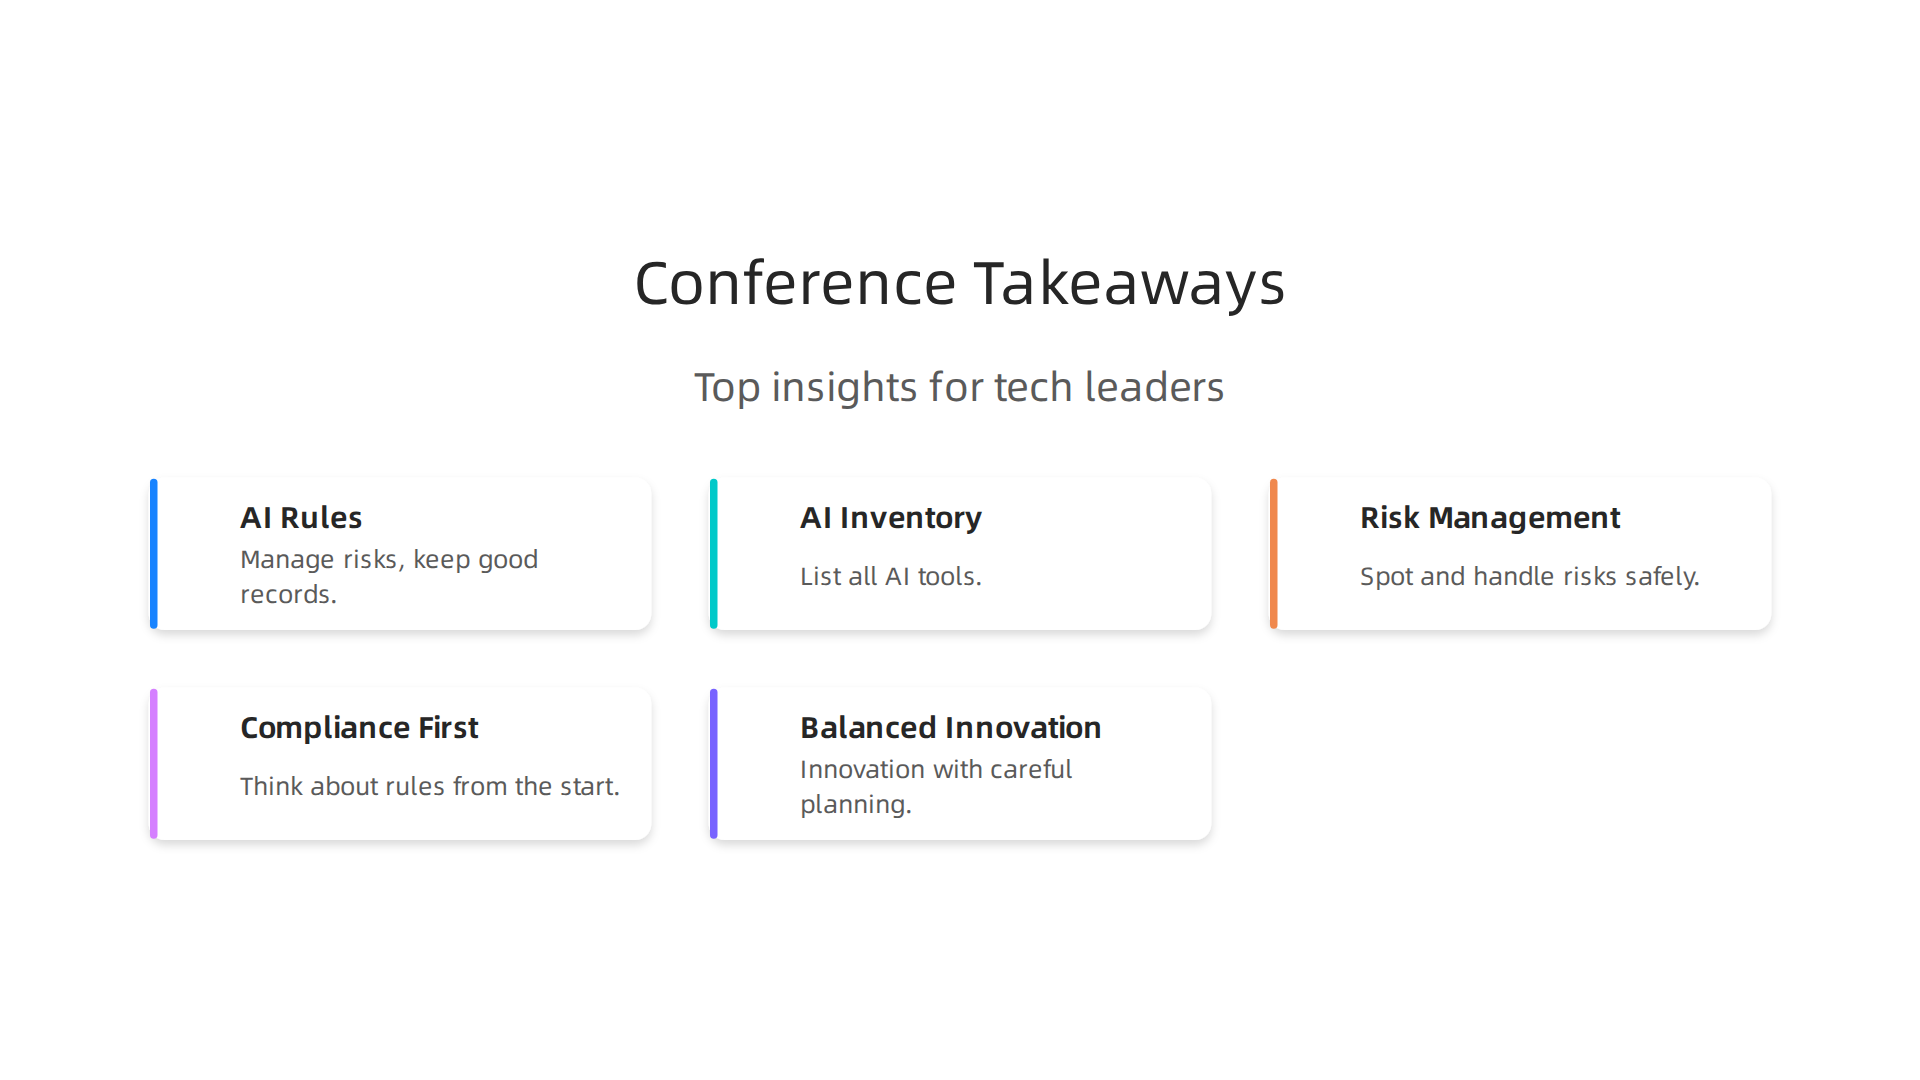
- New Rules for AI are Here: One of the biggest topics was the fast growth of AI and the many new rules coming with it. In 2026, many states have already put in place rules for AI that ask companies to manage risks and keep good records for their AI systems. Companies need to know which rules apply to their AI systems based on where they are used and developed [1]. There are also global efforts, like the EU AI Act, which will start to be enforced in August 2026, especially for high-risk AI tools. This means businesses must show how they plan to meet these rules, perhaps by following a special code of practice. For a deeper look at these changes, check out our guide on AI Regulation 2026 navigate compliance and avoid risks.
- Smart Ways to Handle AI: To keep up, businesses should make a full list of all their AI tools. This list should include who owns them, what they are used for, how risky they are, and how they follow the rules. There are even international standards like ISO/IEC 42001, which is the first global standard for managing AI systems and helps companies build, use, and improve their AI tools safely [2].
- Risk Management is Key: With more tech, comes more risk. Leaders need to know how to spot and handle risks, especially with AI and keeping data safe. Cyber attacks, scams, and fraud are growing, making the risk landscape tricky for big companies dealing with many different laws. This also includes how new technologies affect older ones.
- Compliance Needs to Be First: It is not enough to just make new tech. Companies must think about following the rules from the very start. This means showing what types of AI models are used, what data they rely on, and who is in charge of managing risks. You also need clear records of every time AI uses data, showing what was accessed and when, so it cannot be changed later. Building AI systems that are safe and follow the rules from the start is very important for success. You can learn more about how to build robust AI design test and monitor compliant AI systems in 2026.
- Balancing New Ideas with Rules: The conference made it clear that while innovation is great, it must go hand-in-hand with careful planning for rules. This affects everything from how you design new products to where you decide to sell them and what rules you prioritize. This balance is especially important as we see more news about things like quantum computing news today and other cutting-edge developments.
These takeaways from the texas technology conference mean that leaders in 2026 must be proactive. They need to understand that AI is not just about cool new features, but also about careful management and strict rule-following to avoid big problems and costs. It’s about staying on top of the news, whether it’s about foxconn news, del tech news, or changes in how to handle classified technologies.
Major regulatory announcements and proposed rules discussed
The texas technology conference was not just about talking about new ideas; it also shared important news about rules that are already in place or are coming soon. Many talks focused on what leaders need to do to follow these rules.
Here in Texas, regulators are very busy. For example, the Texas Attorney General has been actively working on cases about privacy. They look closely at how companies collect and use data, especially from people who might be easily taken advantage of. The Attorney General is seen as a leader in making sure data privacy rules are followed Privacy Legislation in Texas: What Happened in 2025 and…. This means if your business handles personal data, you need to be very careful and transparent. They have even used consumer protection laws against some big tech companies, including television makers, when their practices were not fair.
Other state agencies are also taking action. In 2026, many departments have issued warnings and taken steps to make sure businesses follow the rules. This includes environmental agencies, which report thousands of violations and millions of dollars in fines for not meeting standards TCEQ Monthly Enforcement Report – FY26 through January. The Office of Consumer Credit Commissioner also lists enforcement actions taken against different companies, showing how busy regulators are across many areas Enforcement Actions.
These actions show a clear trend: companies must be ready for regulators to check their work. This applies to all kinds of new technology, including those related to quantum computing news today, and how companies handle sensitive or classified technologies. It’s not just about what is new, but also about making sure existing laws are followed.
Looking ahead, we can expect more proposed rules, especially for AI. While federal rules are still developing, states like Texas are moving quickly. The general idea is to make sure AI is used safely and fairly, with clear ways to manage risks and keep good records. This will likely lead to more detailed rules on how AI systems are built, tested, and used. For a broader view of how these changes are happening across the country, you might want to read about US Tech Regulations 2026 navigating data privacy ai governance and antitrust rules.
The conference made it clear that leaders in technology need to keep up with these announcements and trends,
whether it’s about foxconn news or del tech news. Staying informed helps businesses avoid problems and plan better for the future.
To keep up with these important changes every day, consider subscribing to The AI Newsletter Worth Reading for clear daily updates.
AI governance sessions: standards, safety, and enforcement
The discussion about rules at the texas technology conference went deeper, especially when it came to Artificial Intelligence, or AI. While many talks focused on general rules, specific sessions looked at how we can make AI systems safe and fair. These talks highlighted important standards, safety plans, and how new rules will be put into action.
Many states are now setting up their own AI rules. For example, some states have already started enforcing laws in late 2025 and into 2026. These rules ask companies to manage risks, keep good records, and watch over their high-impact AI systems 2026 AI Laws Update: Key Regulations and Practical Guidance. This means if you are making or using AI, you need to know what these rules expect from you.
At the conference, there was a lot of talk about special blueprints for AI governance. These are like rulebooks that help companies make sure their AI is working correctly and safely. Two important ones that gained a lot of attention were:
- ISO/IEC 42001: This is the first worldwide standard for managing AI systems. It gives companies a clear way to build, use, and improve their AI while following rules. It is something that can be checked by outside experts to show your company is doing things right. You can learn more about different approaches to making AI safe by reading about 7 AI Governance Frameworks You Should Know in 2026 (NIST, ISO …).
- NIST AI Risk Management Framework (AI RMF): This framework helps organizations figure out and handle the risks that come with AI. While it is mostly a guide, it is becoming very important, especially for government groups in the US.
For businesses and teams that build products, these frameworks are super important. They mean that companies need to keep a full list of all their AI systems, understand what risks each one has, and know which rules apply. It also means that for any new quantum computing news today, or even older classified technologies, the way they use AI needs careful thought and planning. Businesses need to prepare for rules that will ask them to show how they keep AI safe, fair, and easy to understand. This is true whether you are following del tech news or foxconn news.
To get ready for these new rules, companies should focus on a few key things:
- Keeping good records: You need to document how your AI systems make decisions.
- Checking for risks: It’s important to find and fix any possible harms your AI could cause.
- Building trust: Make sure people can understand how your AI works and why it makes certain choices.
Learning how to build robust AI design test and monitor compliant AI systems in 2026 is now a must for every tech company. The conference made it clear that understanding and using these governance plans is not just a suggestion; it is essential for avoiding problems and making sure AI helps everyone. It is all about how to control AI effectively business strategies for global compliance in today’s world.
Key AI frameworks and where they overlap
To truly control AI effectively, as we discussed, understanding the core frameworks is key. The Texas technology conference really made this clear. While both ISO/IEC 42001 and the NIST AI Risk Management Framework (AI RMF) help guide how we use AI safely, they work in slightly different ways.
Think of ISO/IEC 42001 as a rulebook for setting up an entire AI management system. It is a worldwide standard that you can get certified for, showing that your company follows best practices for building and using AI. It helps make sure your AI processes are managed well, from start to finish. On the other hand, the NIST AI RMF is more like a helpful guide to spot and deal with risks that AI might create. It is especially important for government groups in the US, telling them how to think about AI dangers and how to make AI safe. Both frameworks want the same thing: AI that is safe, fair, and trustworthy. But ISO gives you a structure to manage AI, and NIST gives you tools to manage its risks.
For companies making products, this means you need to look at each feature of your AI and see how it fits into these rules. For example, if your product uses AI, you need to know how ISO/IEC 42001 says you should manage its development. You also need to know how NIST AI RMF wants you to handle any risks from that feature. This often means keeping a clear list of all your AI systems, understanding the possible risks of each, and linking your product features to the rules. This kind of careful planning is needed for all new tech, from exciting quantum computing news today to managing older classified technologies in 2026. To make sure you’re doing this right, you might need a plan to integrate regulatory compliance into your corporate AI strategy. Businesses need to track how their AI systems make decisions, manage who is in charge of risks, and show how they monitor quality and performance AI Governance Frameworks in 2026: What Compliance Demands. This is true whether you’re reading Del Tech news or Foxconn news.
Staying on top of these complex and always-changing AI rules can be hard.
Get clear daily AI updates from The AI Newsletter Worth Reading.
Privacy, data protection, and cross-border compliance
Actually, one of the trickiest parts of these rules involves how we handle people’s private information. At the recent texas technology conference, many talks focused on privacy, data protection, and how tough it is to send data across different countries while staying compliant. It’s not just about AI anymore; it’s about protecting every piece of personal data.
New privacy laws are popping up fast. For example, in the US, new state privacy laws in Indiana, Kentucky, and Rhode Island all started this year, 2026, adding more rules for businesses to follow Data Privacy Developments in 2025 and Compliance Considerations for 2026. This means businesses must constantly update their privacy practices to match these new state-by-state rules. On top of that, the Texas Attorney General is very active. They are looking closely at privacy problems, especially how data is collected from people who might be more at risk Privacy Legislation in Texas: What Happened in 2025 and …. You might even see this type of strict enforcement highlighted in general del tech news.
The challenges don’t stop at state borders. Moving data across countries has become much harder. Rules like the EU’s General Data Protection Regulation (GDPR) and the new EU AI Act, which fully takes effect in August 2026, add extra layers of complexity for international data transfers Five inflection points in 2026 cross-border data governance. Companies now need to be very careful when moving American personal information across borders, as this comes with higher legal risks Cross-Border Transfers of American Personal Information Carry Heightened Regulatory Litigation Risks. Even countries like China are getting tough, with regulators enforcing strict rules on cross-border data transfers CHINA: China’s Data Regulator Means Business. For businesses, understanding these global changes is key to mastering global AI regulations 2026.
What does all this mean for your business?
- Data Transfers: You must have a clear legal reason for every time you transfer data. This is true whether you’re dealing with customer data or product data.
- Vendor Contracts: You need to make sure that any company you work with also follows all the data protection rules. Their compliance is now your problem too.
- Product Telemetry: If your product collects information about how users use it (telemetry data), you need to be very clear about what you collect, why you collect it, and get proper consent.
Navigating these rules means putting new strategies in place for how you handle data. This includes understanding US tech regulations 2026 and ensuring your systems allow for transparency. Companies must also check how their AI systems use voice data, given the AI voice generation legal ethical risks. This complex legal landscape makes compliance a top priority for any business using technology today.
Practical compliance steps highlighted
So, how do businesses actually tackle these tough new rules? Leaders at events like the texas technology conference talk about practical ways to make sure their companies follow the law. It means taking clear steps to manage data, not just hoping for the best.
First, you need a full "data inventory." This means making a list of all the personal information your business collects, stores, and shares. For each piece of data, you must know why you have it and if you have a legal reason to keep it Guidance Note on Cross-border Data Transfers. This helps you handle sensitive or even classified technologies data correctly.
Next, you should do Data Protection Impact Assessments (DPIAs). These are like check-ups to find and fix any privacy risks before they become a problem. Also, remember that your partners’ data habits affect you. You must carefully check that any company you work with, like cloud providers or software vendors, also follows all data protection rules. Their slip-ups can become your big fines. Keeping up with del tech news can offer important updates on these kinds of issues.
Here is a short checklist for executives to prioritize near-term tasks for compliance in 2026:
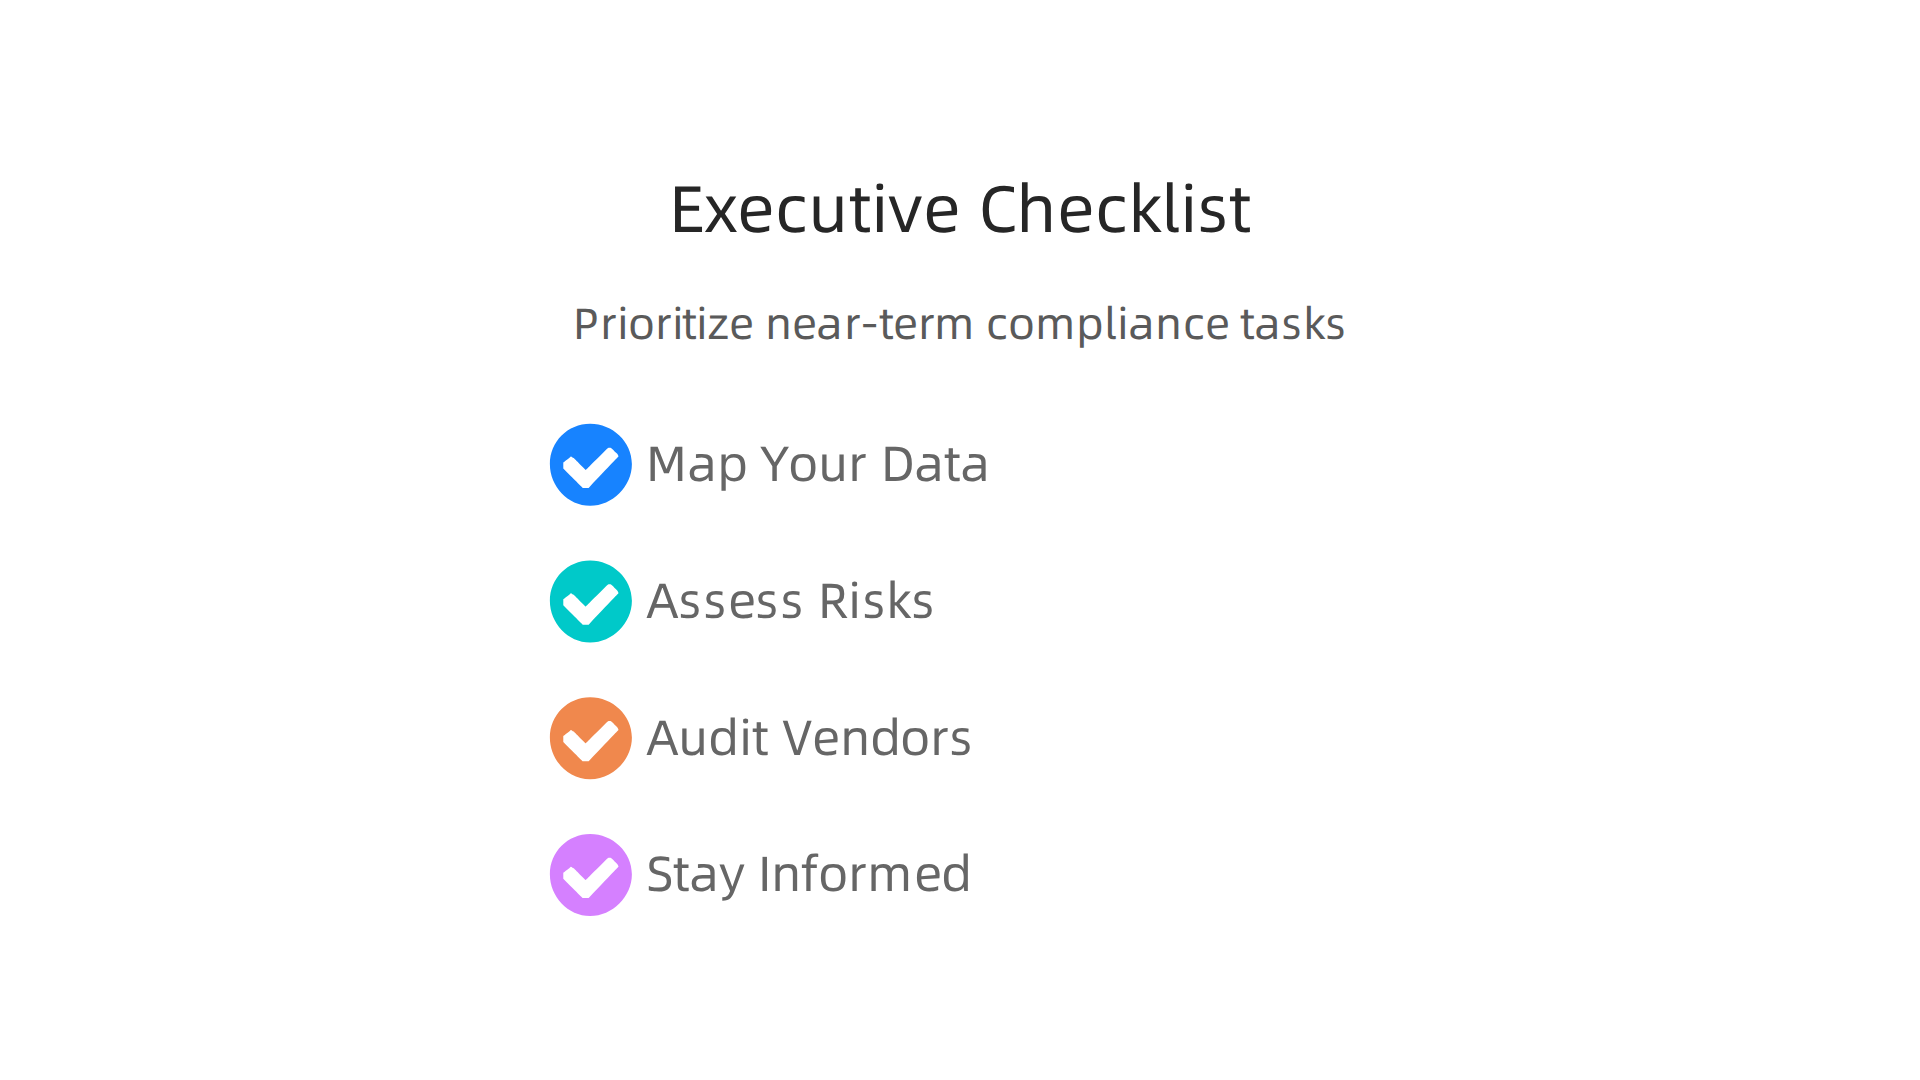
- Map Your Data: Understand every piece of personal data flowing in and out of your business.
- Assess Risks: Regularly check for privacy risks and fix them fast.
- Audit Vendors: Make sure all your third-party partners are also compliant.
- Stay Informed: Keep an eye on new laws and rules, especially for cross-border data transfers Global Data Privacy Laws 2026: Cross-Jurisdiction ….
These steps are key to avoiding big problems and ensuring your business stays on the right side of the law. To learn more about managing sensitive data and ensuring your tech strategies are compliant, read our guide on Mastering Oversight of Classified and Sensitive Technologies for 2026 Compliance.
Staying ahead of the ever-changing world of tech regulation can feel like a full-time job. For clear, daily updates that cut through the noise, consider subscribing.
The AI Newsletter Worth Reading
Investor and market implications
Understanding and following new tech rules isn’t just about avoiding trouble. It also changes how big money thinks about investing.
When companies take strong steps for data protection and compliance, it makes them more attractive to investors. This is a big topic at events like the texas technology conference, where leaders discuss how enforcement trends and new laws affect where money goes.
New rules, especially for things like classified technologies and data privacy, directly impact how much a company is worth. If a company doesn’t follow these rules, it faces big fines and a bad reputation. This makes investors think twice. On the other hand, companies that build strong compliance into their plans from the start often look much safer. This changes their "valuation," which is what investors think the company is worth. For example, the market for "RegTech," which is technology that helps companies comply with rules, is growing fast and is expected to reach $24.67 billion by 2030 Regulatory Technology Market Report 2026. This shows that compliance is a serious business.
For venture capitalists (VCs) and their young companies, these changes bring both dangers and chances to grow. Panels at tech events often highlight new areas of risk. These include:
- Higher Costs: Making sure all systems follow the rules can cost more money and time.
- Market Entry Challenges: New products might face delays if they do not meet strict data or AI regulations right away. Keeping an eye on
del tech newscan give early warnings about these issues. - Data Security: Cyber attacks are still a major risk for businesses, especially with new tech like AI, leading to more data protection concerns for investors Tech Legal Outlook 2026.
But there are also great opportunities. Companies that create smart ways to manage data and meet rules can stand out. For example, businesses focusing on ethical AI or secure quantum computing news today could attract a lot of investment. News about companies like foxconn news often includes updates on how they are adapting to global rules, setting examples for others. Investors are looking for companies that don’t just innovate, but do so responsibly. They want to see clear plans for handling AI safety risks and making sure their technology is used in a good way. If you are an investor or tech leader, it is important to Clarify AI Safety Risks a Literature Review for Tech Leaders and Investors to understand these complex issues.
In 2026, staying ahead of regulatory changes is not just a legal task. It is a key part of business strategy and how companies are judged in the market.
Actionable next steps for executives and compliance teams
Since being prepared for new tech rules is now a big part of how companies succeed in 2026, leaders and their teams need clear steps to follow. After attending important events like the 2026 Texas Technology Summit, it is time to turn what you learned into real actions. Here is a simple plan for your product, legal, and compliance teams.
Short-Term Steps (Next 3-6 Months)
Your main goal in the short term is to get a clear picture of what you are doing now and where new rules might cause problems.
- Review New Laws: Many new privacy laws came into play in January 2026, including in states like Indiana, Kentucky, and Rhode Island. Your team should check these and other new rules, such as those impacting cross-border data transfers, to see how they affect your business Data Privacy Developments in 2025 and Compliance Considerations for 2026.
- Map Your Data: Find out exactly what data your company collects, stores, and uses. This helps you know which information falls under new privacy rules. This is very important for any
classified technologiesyour company might handle. Knowing your data makes it easier to follow rules about sensitive information. - Improve Audit Trails: Make sure you can track all data changes and who accesses it. Having a single, real-time system for audit logging across all your data channels is a smart move for 2026 Global Data Privacy Laws 2026: Cross-Jurisdiction Data Sharing Compliance.
- Assign Clear Roles: Who is in charge of checking data privacy? Who makes sure AI tools are used correctly? Give specific people these jobs. This helps avoid confusion and makes sure someone is always watching for new risks.
Medium-Term Steps (Next 6-12+ Months)
Once you have a basic understanding and some fixes in place, you can work on stronger, lasting solutions.
- Build Stronger Rules: Create clear company rules that everyone can follow to meet global data privacy and AI requirements. Think about how to integrate regulatory compliance into your corporate AI strategy right from the start.
- Train Your Staff: Teach all your employees about the new rules and why they matter. When everyone understands, it is much easier to stay compliant.
- Look to the Future: Keep an eye on
del tech newsand other sources for hints about upcoming regulations. Companies that work with advanced areas likequantum computing news todayneed to plan even further ahead. - Automate Compliance: Use technology to help you keep track of rules and make sure you are following them. This is where "RegTech" comes in, offering tools to manage tricky tasks like international data transfers Navigating International Data Privacy Compliance in 2026. Also, learn about mastering oversight of classified and sensitive technologies for 2026 compliance to keep important data safe.
- Learn from Others: Watch how big companies like those in
foxconn newshandle global regulations. Their approaches can offer lessons for your own plans.
By taking these steps, your team can move from just reacting to rules to being leaders in safe and fair tech use. This will protect your company and help it grow in the busy tech world of 2026.
To keep up with the latest daily news and insights on AI and technology rules, you need trustworthy information. Get clear daily AI updates from The AI Newsletter Worth Reading.
Getting ready for new tech rules is a continuous effort. While the last section talked about steps for the short and medium term, sometimes you need a quick plan to kick things off. Here is a simple 90-day checklist to help your teams move fast, based on what is often shared at events like a texas technology conference. This plan tells you who should do what and what success looks like right away.
90-day action checklist
- 1. Find New Laws (Owner: Legal/Compliance)
- What to do: Pinpoint the newest privacy laws and AI rules that affect your business the most. For example, staying updated on events like the DALLAS TECHNOLOGY SUMMIT 2026 can provide quick insights.
- Success looks like: A clear list of 3-5 key new laws and a short note on how each one might change your company’s work.
- 2. Start Data Mapping (Owner: Product/Compliance)
- What to do: Begin figuring out what main types of data your company handles for its most important products and services. Think about any
classified technologiesthat need special care. - Success looks like: An initial map or list showing your company’s core data types and where they are used.
- What to do: Begin figuring out what main types of data your company handles for its most important products and services. Think about any
- 3. Name Your Tech Watchdogs (Owner: Executive/Legal)
- What to do: Officially name people responsible for data privacy and for making sure AI tools are used ethically and legally. This is about making sure someone is always on watch.
- Success looks like: Specific names assigned to these important roles across your teams.
- 4. Quick Check for AI Risks (Owner: Product/Legal/Compliance)
- What to do: Do a fast review of any AI tools or sensitive technologies your company uses right now. Look for any immediate risks with how they collect or use information.
- Success looks like: A simple report that points out any big risks found and suggestions for quick fixes. To learn more about handling sensitive information, explore understanding classified technologies in 2026 what businesses must know about export controls and compliance.
- 5. Local Tech Pulse Check (Owner: Executive/Legal/Compliance)
- What to do: Pay attention to local tech events and news. For instance, a Primer on Texas’ Largest EdTech Convention can show you what local leaders are thinking.
- Success looks like: Your team has reviewed at least one local tech event summary or key
del tech newsarticles to grasp regional trends.
By following this fast-paced checklist, your company can build a strong foundation for managing tech rules in 2026, making sure you are both safe and ready for what is next.
Summary
The article distills the most important lessons from the 2026 Texas technology conference for leaders, investors, and compliance teams, focusing on how rapid advances in AI, cybersecurity and emerging tech intersect with new rules. It summarizes key regulatory developments—state-level enforcement, the incoming EU AI Act, and growing expectations for documentation and risk management—and explains why frameworks like ISO/IEC 42001 and the NIST AI RMF matter. The piece covers practical next steps: create an AI and data inventory, run DPIAs, tighten audit trails, assign clear owners, and use RegTech where possible. It also outlines a 90‑day plan and longer‑term measures to embed compliance into product strategy, and it flags investor implications such as valuation and RegTech opportunity. Overall, readers will learn what to prioritize now to reduce legal and market risk, how to prepare for cross‑border data rules, and how to turn conference insights into concrete actions for 2026.