Why Corporate AI Strategy Must Be Inseparable from Regulatory Compliance
In 2026, the world of Artificial Intelligence (AI) is moving faster than ever. New AI tools and platforms are changing how businesses work every day. But with all this speed comes a big challenge: laws and rules about AI are also changing very, very fast. This means companies using AI, from small startups to "big tech" giants, face many new risks. If you don’t keep up, your company could run into big problems with the law, lose money, or even harm its reputation.
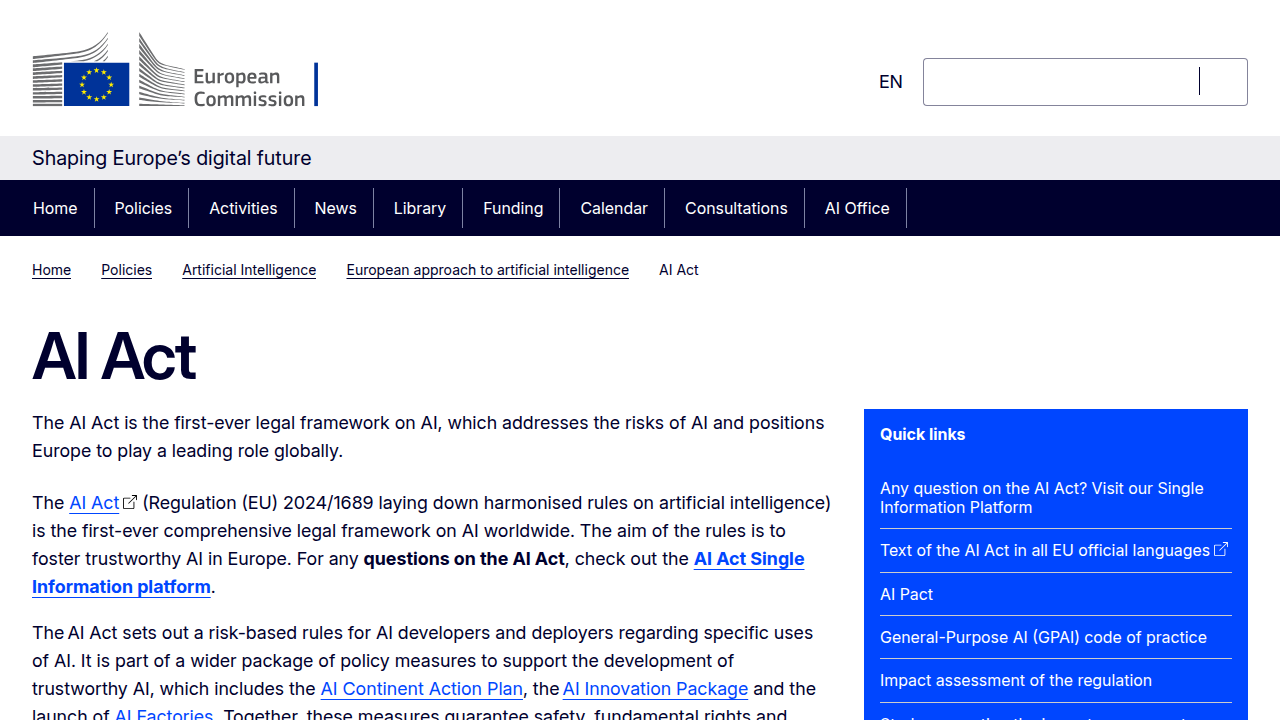
Think about it: countries like the European Union have a major law called the AI Act | Shaping Europe’s digital future – European Union that fully goes into effect this year.
In the US, states like California and Colorado have their own specific AI laws. This creates a complex puzzle for businesses to solve. You need "clarity ai" in your plans to make sure your AI products and services meet all these new rules.
Without a clear plan, what seems like a great AI agent platform today could become a huge liability tomorrow. In fact, experts say there are over 1,000 AI policy rules being tracked globally in 2026, making AI Governance and Regulation 2026 a complete guide for businesses.
This fast-moving world of AI regulation causes both strategic and daily operational risks for technology companies. It’s not enough to just make the best AI tools for businesses. You also need to make sure they are legal and ethical. This can feel overwhelming, but it’s a must-do.
This guide will give you a clear, practical roadmap. We will show you how to connect all your legal duties to how you create products, how you run your company (we call this governance), and what your investors care about. Our goal is to help you understand how to navigate these challenges so you can succeed and stay safe in the AI world of 2026. For more help with these rules, learn how to navigate AI regulation 2026 compliance and avoid risks and understand the tech regulations 2026 global changes tech leaders must understand.
Staying up to date with these rapid changes is crucial. To get clear daily AI updates directly to your inbox, consider subscribing to The AI Newsletter Worth Reading.
Map the global regulatory landscape: priorities for executives and investors
To truly succeed with AI in 2026, business leaders and those who invest in companies need to know where the most important AI rules are coming from. It’s like having a map for a big trip.
You need to know which roads are busiest and which ones might have unexpected turns. This understanding brings much-needed clarity to AI plans.
The European Union’s AI Act is a very big deal. It will fully start on August 2, 2026, and it sets many new rules for how AI systems must work. But it’s not just Europe. In the United States, there’s no single big federal law for AI yet. Instead, states like California, Colorado, New York, and Texas have their own rules. For example, Texas has the Responsible Artificial Intelligence Governance Act, and Illinois has rules for AI in hiring. You can find more details about these state laws in an overview of US AI regulations for 2026. This means businesses selling AI products across the US need to keep track of many different state requirements.
Other countries are also making their own rules. The United Kingdom, for instance, is taking a different approach, aiming for a pro-innovation approach to AI regulation. Australia is also changing its stance on AI rules, as noted in an Australian AI Update.
For executives and investors, it is important to focus on key areas that these rules often cover:
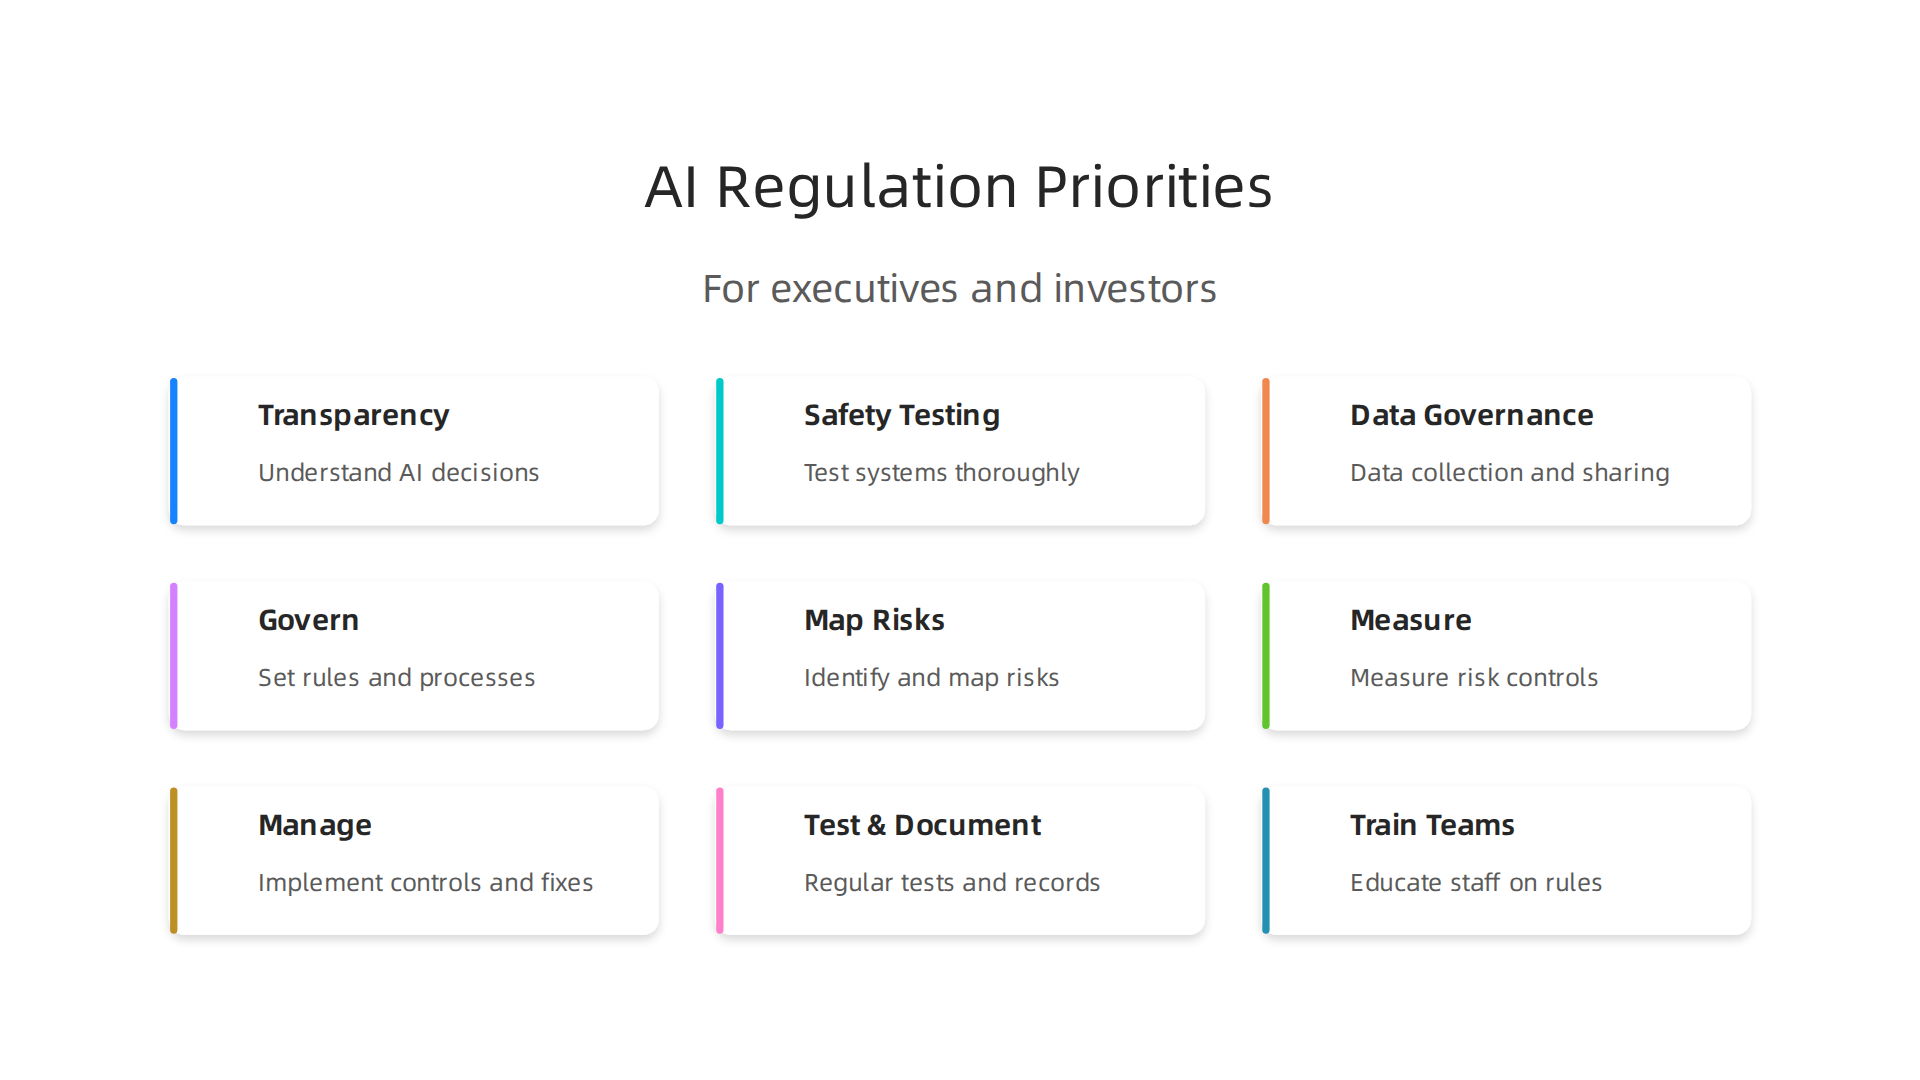
- Transparency: This means that people should understand how AI decisions are made. If an AI agent platform makes a choice, companies need to be able to show how it got to that answer. This is especially true for systems that affect people’s jobs, healthcare, or safety.
- Safety Testing: AI systems, especially those that could cause harm (called "high-risk" AI), must be tested thoroughly to make sure they are safe and work as expected.
- Data Governance: This involves how data is collected, stored, used, and shared with AI. Companies must follow strict rules about protecting personal information and ensuring the data used to train AI is fair and unbiased.
If you are a technology executive or investor, getting a comprehensive guide to AI laws and regulations worldwide helps your product roadmaps. It also means building the right processes inside your company. Many of the best AI tools for businesses today focus on helping companies track and prove their AI systems are working correctly and safely. This level of clarity in AI operations helps avoid problems and builds trust, which is important for big tech companies and smaller startups alike. For more detailed insights, you can watch AI Rules Are Changing: Key Regulatory Updates from 2025 and beyond.
Now that we understand the big picture of AI rules around the world, the next step is to make those rules real for your business. It’s not enough to just know what the laws say. You need a clear plan to turn those legal words into everyday actions for your company. This helps bring real clarity to AI operations.
First, you need to figure out the exact things your company must do, which are called "obligations." Then, you need to know what your company must not do, which are "prohibited behaviors." For example, if a law says your AI agent platform must explain its decisions, your team needs to build that explanation feature into the product. If a law says your AI cannot be used for certain unfair choices, then your product design needs to block those uses.
A really important part of making laws into company rules is keeping good records. This means you need to show how your AI systems follow the rules. You need to document how you test them, how you handle data, and how you make sure they are fair. Without proper documentation and recordkeeping, it’s hard to prove your company is doing the right thing.
To help businesses with this, there are helpful guides, like the AI Risk Management Framework from NIST. This framework gives clear steps to manage AI risks. It helps companies get clarity AI by breaking down big rules into smaller, manageable tasks. The NIST AI RMF uses four main ideas to help you:
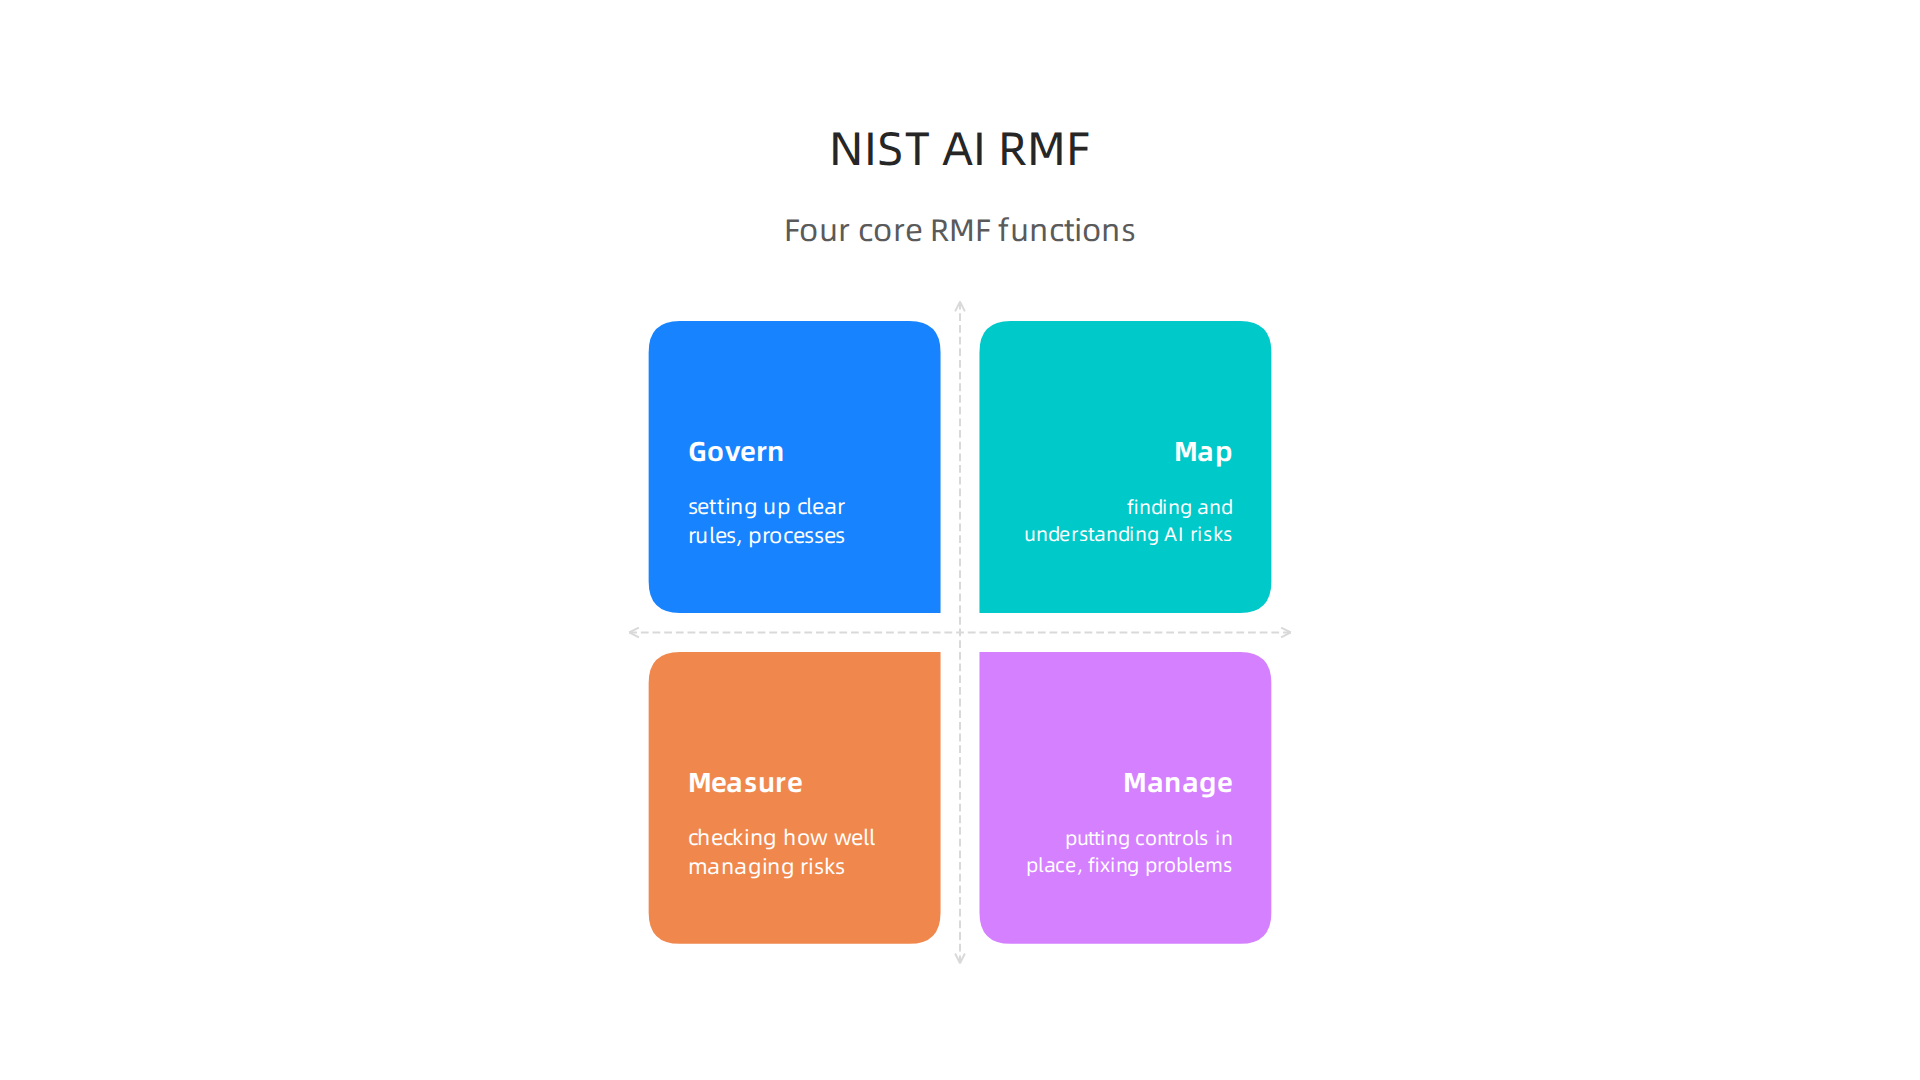
- Govern: This means setting up clear rules, processes, and who is in charge of what regarding AI risks. It asks, "Who owns the risk when this system fails?" It is about having policies and procedures in place across the organization related to how AI risks are handled. You can learn more about the Govern function in AI RMF 2026.
- Map: This is about finding and understanding the AI risks in your company’s different systems. It means knowing where AI is used and what problems it might cause.
- Measure: This involves checking how well your company is managing those risks. It’s about setting up ways to track and see if your efforts are working.
- Manage: This is about putting controls in place, watching for new issues, and fixing problems when they happen. This includes implementing controls and responding to incidents, as explained in the NIST AI RMF 1.1 Changes Update 2026.
These four functions help you create important papers, called "governance artifacts." These are like your company’s playbook for AI. They include:
- Policy Statements: These are clear rules for how your company will use AI, making sure everyone knows what is expected.
- Risk Acceptance Decisions: These are records that show when your company decided to accept a certain risk, after thinking carefully about it.
- Decision Logs: These are notes about why certain choices were made for an AI system. If an AI agent platform makes a tricky decision, the log should show how it got there.
By using frameworks like the NIST AI Risk Management Framework and creating these governance artifacts, big tech companies and smaller startups can ensure their AI products meet legal requirements. This structured approach helps in making sure AI systems are used safely and fairly, turning confusing laws into actionable steps. If you want to know more about how to set up your AI for success, you can explore guides on how to build AI systems compliantly in 2026.
Moving from understanding AI laws to actually using them in your business can feel like a big jump. Luckily, there are many tools and guides, called "frameworks," that help companies build strong ways to follow rules. These frameworks give you a clear path forward, leading to greater clarity AI in your daily work.
The NIST AI Risk Management Framework that we just talked about is a very helpful one, especially for businesses in the U.S. It helps you see the big picture of AI risks and how to handle them. But it’s not the only game in town. Other important frameworks exist too. For example, the International Organization for Standardization (ISO) offers standards like ISO/IEC 42001, which is all about AI management systems. This one is recognized around the world and can be great for global companies or those who want to show they meet international best practices. There’s also the Cloud Security Alliance (CSA) Artificial Intelligence Controls Matrix (AICM), which helps if your AI uses cloud services a lot.
Choosing the right mix of these frameworks helps you create what’s known as a "defensible compliance stack." This means you have clear systems and records that prove your AI efforts are fair, safe, and follow the law. It’s like having a shield of proof. For big tech companies and even smaller startups, these frameworks provide a roadmap for AI governance. The NIST AI RMF Playbook, for example, offers suggested actions to achieve the goals of the framework.
To really put these ideas into action, here is a simple plan for your product teams:
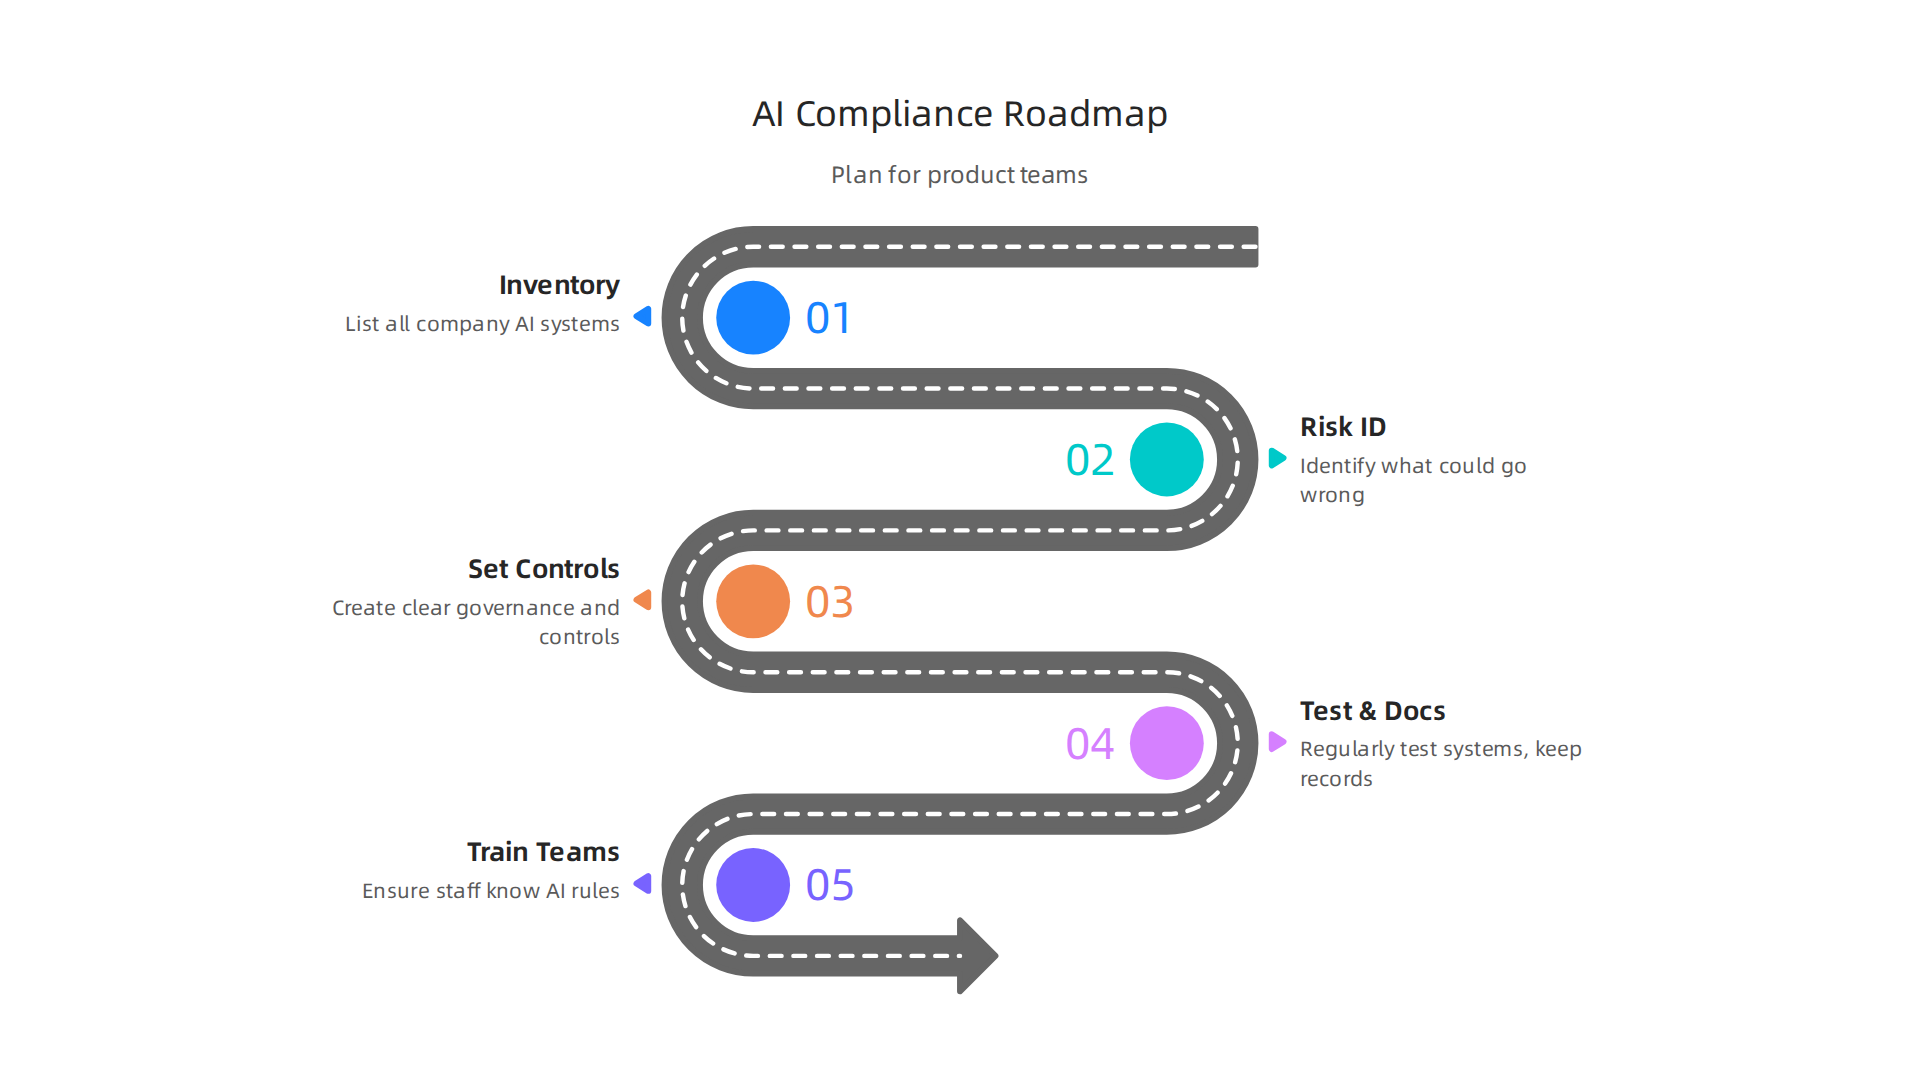
A Clear Roadmap for AI Compliance
- Know Your AI Systems: First, make a list of all the AI systems your company uses or plans to use. Figure out what each one does, what kind of data it uses, and who might be affected by it. This step is like the "Map" part of the NIST framework, helping you see where AI is at play in your business.
- Find the Risks: For each AI system, think about what could go wrong. Could it be unfair? Could it make mistakes? Could it share private information? This connects to the "Measure" function of the NIST AI RMF, where you identify and assess potential harms.
- Set Up Rules and Controls: Based on the risks you found, create clear rules for how your AI should work. This involves setting up who is responsible for different parts of your AI, putting checks in place to stop problems, and deciding what to do if a problem happens. This covers the "Govern" and "Manage" aspects of the framework. For instance, make sure your AI agent platform has built-in ways to check for fairness.
- Test and Document Everything: Regularly test your AI systems to make sure they are still working as they should and following the rules. Keep good records of all your tests, policy changes, and important decisions. This paperwork is super important for showing you’re compliant. A good AI governance guide can show you how to map NIST AI RMF to controls.
- Train Your Teams: Make sure everyone who works with AI knows the rules and understands their part in keeping things safe and fair. Regular training helps keep everyone on the same page.
By following these steps, you can create a strong compliance program that makes sense for your business, ensures clarity AI, and helps avoid costly mistakes. This approach also prepares you to integrate the best AI tools for businesses in a way that truly follows the rules. This helps you figure out how to make an AI compliant with global regulations in 2026.
After you’ve got your AI compliance plan in place, the next big step is making sure you actually follow it. This means regularly checking for problems, getting ready for outside reviews, and knowing what to do if a government agency comes calling. It’s all about making sure there’s real clarity AI in your business, from top to bottom.
Risk Assessment, Audits, and Preparing for Enforcement
First up, let’s talk about AI risk assessment. This is a special way to look at your AI systems and figure out what might go wrong. It’s more detailed than the "Find the Risks" step we talked about earlier. Here’s a simple way to do it:
- Figure out what to look at: Start by deciding which AI systems need a close look. Some AI systems are more important or affect more people, so they’ll need more attention.
- Think about what could happen: Imagine all the bad things that could occur. Could the AI make a wrong decision that harms someone? Could it be unfair to certain groups? This helps you see where the dangers are.
- Map your safety checks: For each possible problem, think about the rules and controls you’ve put in place. Do these controls actually stop or lessen the problems you found? This is like checking if your safety net is strong enough. You can learn more about this by reading our guide on AI Regulations 2026: Navigate Compliance and Avoid Risks.
- See what risks are left: After all your safety checks, what risks still remain? These are called "residual risks." You need to know these so you can decide if they are acceptable for your business.
Getting Ready for Audits and Regulators
Even if you’re doing everything right, outside groups might want to check your work. These could be auditors or government regulators.
Auditors are like independent checkers. They want to see proof that your AI systems are fair, safe, and follow the rules. They’ll look at your records, your testing results, and how your teams are trained. For big tech companies, these audits are a regular part of business. Good records are your best friend here.
Regulators are government groups that make sure businesses follow the law. In 2026, groups like the Federal Trade Commission (FTC) are very active in checking how companies use AI. The FTC has even started a new chapter in how it handles AI enforcement, looking closely at what companies say their AI can do and how they use people’s data The FTC enters new chapter in its approach to artificial …. States are also stepping up with their own AI rules, which means enforcement is speeding up everywhere AI Enforcement Accelerates as Federal Policy Stalls and States Step In.
To be ready for them, make sure:
- You have clear records of your AI risk assessments and compliance steps.
- Your AI agent platform and other tools are set up to be transparent.
- Everyone on your team knows their roles in keeping AI compliant.
Having everything in order provides clarity AI to any outside reviewer. This helps you show that you’re using the best AI tools for businesses in a responsible way. It can also help you avoid big fines and keep your company’s good name. Knowing How to Ensure Field AI Compliance in 2026 and Avoid Billions in Fines is crucial for any business working with AI today.
Staying compliant with AI rules isn’t a one-time thing. It’s an ongoing job, like keeping a garden tidy. You need to watch your AI systems all the time to make sure they’re still working properly and following all the rules. This is called continuous compliance. It means having the right tools and ways to report what’s happening so you always have a clear picture.
Monitoring, reporting and tooling: building continuous compliance (including vendor/tool selection)
To keep your AI systems compliant day in and day out, you need to set up special systems. Think of them as your AI’s health monitors and record keepers.
Here are some important parts:
- Telemetry: This is like a constant data stream from your AI. It collects information about how your AI is performing, what decisions it’s making, and what data it’s using. Watching this data helps you spot problems early, giving you real clarity AI.
- Model Registries: Imagine a library for all your AI models. A model registry keeps track of every AI model your company uses, including its version, who built it, what it does, and how it was tested. This is super important because even small changes to an AI can affect how it behaves.
- Testing: Just because an AI worked well when you first set it up doesn’t mean it always will. You need to test your AI systems often to make sure they’re still fair, accurate, and safe, especially as new data comes in.
- Incident Logging: Sometimes, things go wrong. An AI might make a mistake or act in an unexpected way. An incident log is a record of these problems, how they happened, and what you did to fix them. This helps you learn and improve your systems over time.
Having these systems in place helps you create a complete story of your AI’s behavior. This story is often called an "audit trail," and it’s what outside checkers, like auditors and government regulators, will want to see. Many regulations, like the EU AI Act, now require a lot of oversight and clear records of AI decisions and data traceability The Top 5 AI Governance Platforms for Meeting ….
Choosing the Right Tools for AI Compliance
It’s tough to manage all this by hand, especially for big tech companies or those with many AI systems. That’s why many businesses use special AI compliance tools. These tools help automate many of the tasks we just talked about.
When you’re looking for an AI agent platform or other compliance tools, here’s what to think about:
- Evidence Collection: Does the tool automatically gather all the proof you need? This includes data on how your AI works, how it was trained, and all the decisions it makes. Good tools can make this evidence audit-ready, so you’re always prepared for reviews Best AI Compliance Platforms 2026 –– Expert Guide.
- Explainability: Can the tool help you understand why your AI made a certain decision? Regulators want to know that AI decisions aren’t a black box. This is key for showing that your AI is fair and transparent.
- Auditability: Can the tool easily create the reports and records that auditors and regulators need? It should track every step, from how a model was built to how it’s used today. Many leading AI governance solutions offer continuous monitoring and audit trail creation to reduce risk AI Governance Solutions for Regulated Industries: Top 10 ….
- Real-time Monitoring: The best tools can watch your AI as it runs and give you alerts right away if something seems off. This means you can fix problems before they become bigger issues AI Compliance Monitoring: Tools and Best Practices for 2026.
- Integration: Can the new tool work well with the systems you already have? You don’t want to create more work by having many separate systems that don’t talk to each other. Many tools offer features like automation and integration with existing systems to help with regulatory monitoring Top 10 AI Regulatory Monitoring Tools in 2026: Features, Pros ….
There are many different kinds of AI compliance tools available in 2026, from those focused on governance and risk to those that help with specific regulations like the EU AI Act. Some popular options include Centraleyes for AI-powered compliance and Credo AI for model oversight Top 13 AI Compliance Tools of 2026. These tools help businesses make their AI compliant with global regulations. You can also explore how different types of AI, such as What is agentic AI and how it is changing business in 2026, require specific governance.
Setting up these monitoring, reporting, and tooling systems is how you build continuous compliance. It’s how you show that your company is committed to using AI responsibly, not just at the start, but every single day.
Want to stay informed on the latest AI regulations and tools?
The AI Newsletter Worth Reading
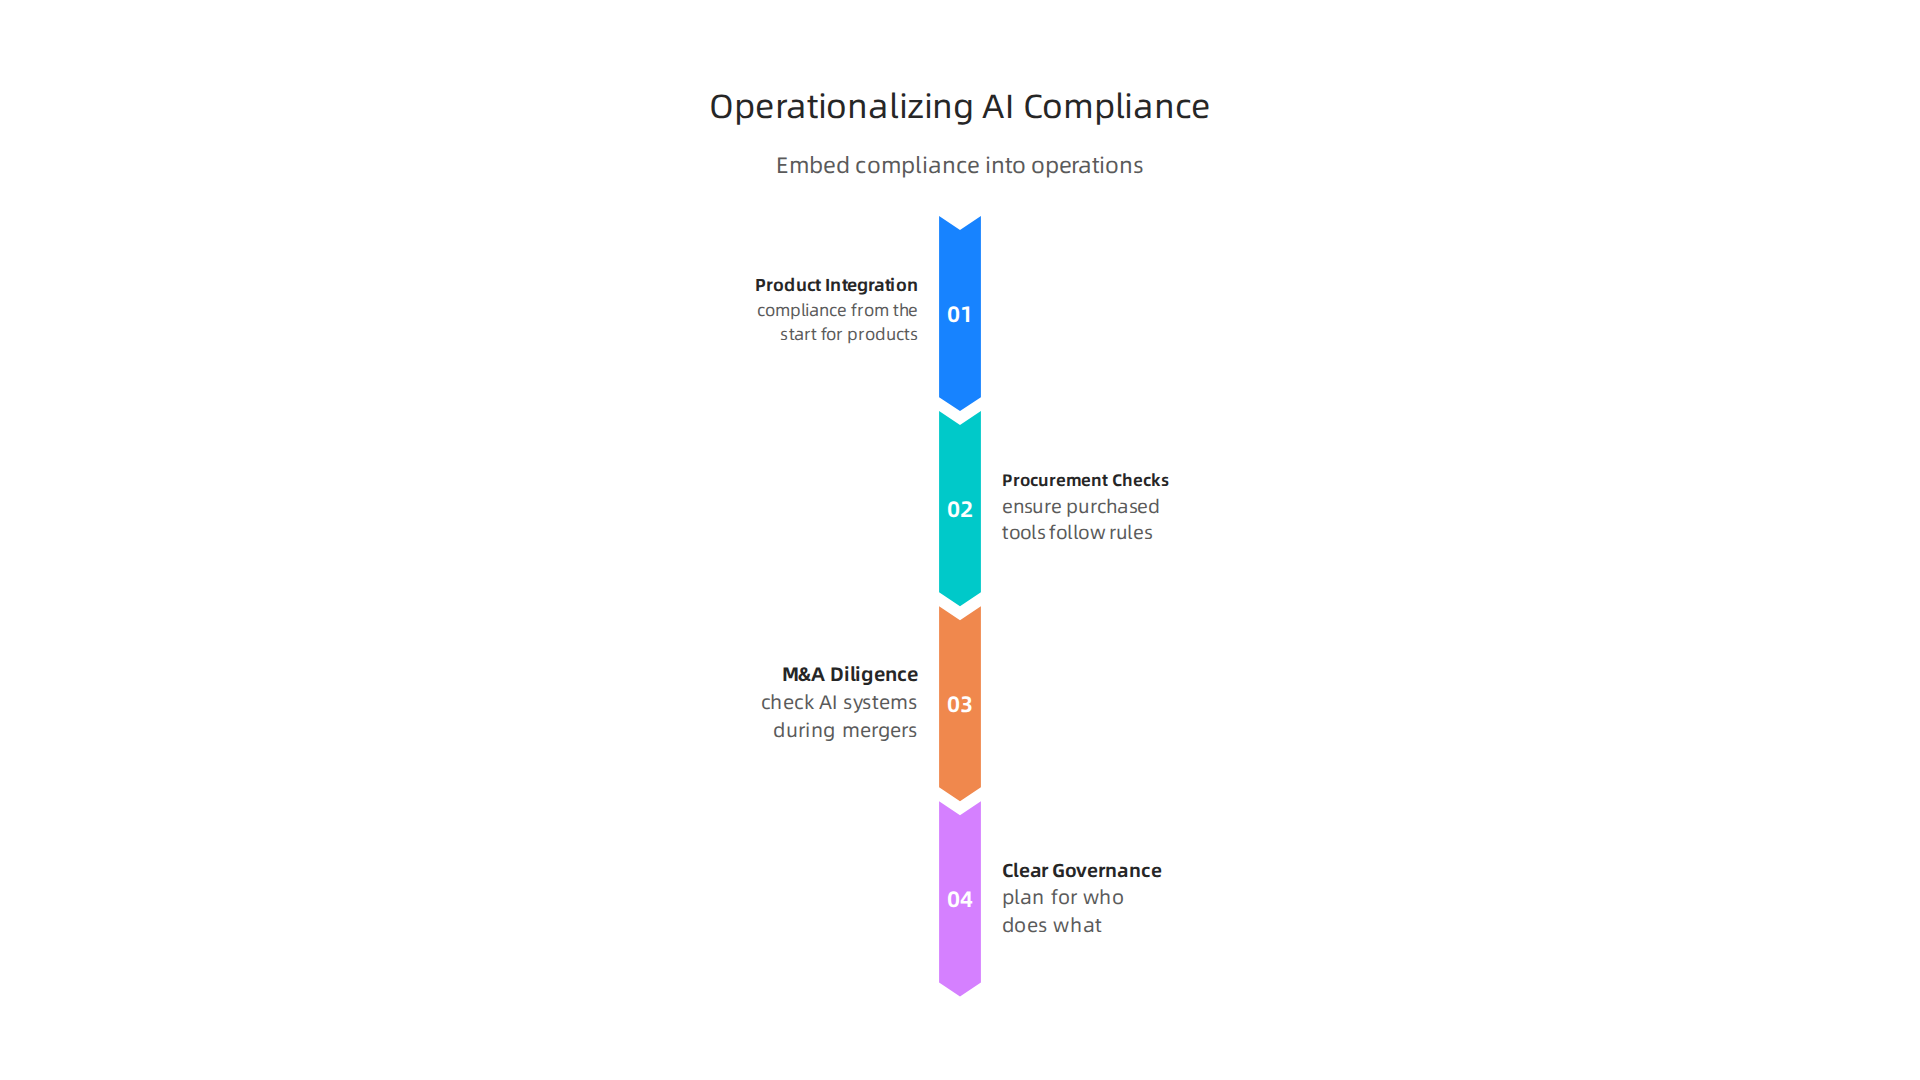
To truly make compliance a part of your company, you need to bake it into everything you do, not just have a separate team handle it. This means thinking about AI rules from the very first idea stage for a new product, when you buy tools from other companies, and even when your company looks to join with or buy another business.
Operationalizing compliance: governance, budgets, and strategic trade-offs
Making AI compliance a core part of your daily work means embedding it deeply into how your business operates.
It’s about setting up smart ways to work, making sure you have the money for it, and making big decisions that balance following rules with growing your business.
Putting Compliance into Your Products
When you build new AI products, thinking about compliance from the start is key. This helps you avoid big problems later. First, you need to find out every AI system your company uses, even those "shadow tools" that employees might be using without official approval. This inventory helps you understand what needs to be governed before you make any rules Enterprise AI Governance: The 2026 Frameworks & Controls Guide.
Next, you must design how decisions are made about AI before you even start using it widely. This helps put controls in place right away AI Governance Framework 2026: A Practical Blueprint for …. Having clear rules and a good system can help you stay compliant with all global AI regulations in 2026.
Checking AI When You Buy Things
When your company buys AI tools or services from other businesses, you need to make sure those tools also follow the rules. This is called procurement. You should ask vendors about their own AI compliance checks, how they handle data, and what safeguards they have in place. This helps ensure that the tools you bring into your company won’t create new compliance risks.
Compliance During Company Mergers and Purchases
If your company plans to merge with another or buy a different business, you must check their AI systems very carefully. This is called M&A diligence. You need to look at their AI policies, how they manage data, and any past compliance issues. This step helps you understand any hidden risks before the deal is done. You can learn more about finding the right tools and strategies by exploring how to build AI systems compliantly in 2026.
Setting Up How Compliance Works (Governance)
Good AI governance means having a clear plan for who does what. In 2026, many big tech companies use a "federated hub-and-spoke model." This means there are central rules for everyone, but each business group also has people responsible for their own AI use Enterprise AI Operating Model Report 2026 | Alice Labs.
Usually, the company’s top leaders, like the board, decide how much risk they are willing to take with AI. Then, special AI teams set the standards. The teams who actually build and use the AI are responsible for making sure it follows those rules every day The CIO’s Playbook for Enterprise AI Strategy in 2026 …. It’s all about making sure there’s clarity AI across the organization.
Paying for Compliance (Budgets and Resources)
Compliance isn’t free. You need to set aside money and people for it. This includes funds for training staff, buying the best AI tools for businesses that help with monitoring, and hiring experts. It’s important to show that the money spent on compliance actually helps the business. For example, good governance can lead to fewer mistakes, faster project launches, and avoiding big fines Operationalizing Enterprise AI Governance in 2026.
Talking About Risk to Leaders
Company boards and investors need to know about the risks of AI. You should explain potential fines from regulators like the FTC or state attorneys general, and how these could affect the company. For example, the FTC is actively enforcing rules against misleading AI claims and data practices related to automated decisions AI Enforcement Accelerates as Federal Policy Stalls and States Step In.
By clearly showing the risks and how your compliance efforts protect the company, you can get the support and resources needed to do things right. This ensures that even in big tech firms, the strategic trade-offs between innovation and compliance are well understood and managed.
Tech Regulation News Today helps you stay informed on the rapidly evolving landscape of AI rules and compliance. Get daily, in-depth AI and technology regulatory insights. Subscribe to The Deep View Newsletter.
Summary
AI is evolving faster than the rules that govern it, and this article explains why corporate AI strategy must be inseparable from regulatory compliance in 2026. It walks executives and investors through the global landscape — from the EU AI Act to diverse U.S. state laws — and translates legal obligations into operational steps your teams can follow. You will learn how to apply risk frameworks (notably NIST AI RMF), create governance artifacts like policies and decision logs, and map, measure, and manage AI risks across products. The guide lays out a practical roadmap for product, procurement, M&A, and audit readiness, plus the tooling and telemetry you need for continuous compliance. It also covers how to prepare for external audits and enforcement, how to choose compliance platforms, and how to budget and govern AI risk across an enterprise. After reading this, leaders will know concrete next steps to reduce legal, financial, and reputational exposure while continuing to deploy AI responsibly.